
The popular advice about web application vulnerabilities is still too focused on finding the next SQL injection or XSS payload. Those bugs matter, but an MSSP that measures success by the number of findings produced is measuring the wrong outcome. The operational failure is often simpler: a known critical issue remains exploitable, ownership is unclear, and nobody verifies the fix across every affected endpoint.
A 2018 web application vulnerability report found an average of 33 vulnerabilities per application, including 6 high-severity issues, while critical vulnerabilities per application had grown 3x compared with 2017 (historical web vulnerability report). The lesson remains relevant in 2026. Risk accumulates quickly, and remediation capacity matters as much as discovery.
Table of Contents
- What Makes Web Application Vulnerabilities Hard to Fix
- Mapping the Modern Threat Landscape
- Exploitation Mechanics and Business Impact
- Detection and Penetration Testing Approaches
- Remediation Workflows and Secure Development
- Compliance Mapping and Audit Readiness
- Scaling Security Operations for MSSPs
What Makes Web Application Vulnerabilities Hard to Fix
Security teams often treat identification as the endpoint of web application security. Operationally, it is the start of a control loop. A scanner produces a finding, a consultant documents it, and the client opens a ticket. Risk falls only when the vulnerable behavior disappears, the correction survives deployment, and retesting proves that the affected workflow remains safe.
Delayed remediation keeps known exposure active. The 2026 State of Application Security report found that 32% of critical vulnerabilities remained open beyond 180 days. Its 2025 reporting also found that 33% of critical and high vulnerabilities stayed unpatched for more than 180 days. These figures point to an ownership and verification failure, rather than a lack of vulnerability definitions.
Practical rule: A finding without an owner, deadline, retest method, and evidence requirement lacks the structure needed for remediation.
Why classic bug hunting is no longer enough
SQL injection and XSS still provide useful test cases because they expose weaknesses in input handling and output control. Modern applications, however, distribute authorization across browser clients, REST services, GraphQL resolvers, microservices, identity providers, and SaaS integrations. A clean page-scan result cannot establish that a user is prevented from retrieving another customer's object through an API request.
One customer record may be available through a user interface, mobile endpoint, background integration, and administrative workflow. Each route can enforce a slightly different permission check. MSSPs therefore need to test authorization consistency across roles, objects, operations, and interfaces, rather than assess URLs in isolation.
API exposure increases the verification burden. The 2026 application-security research cited above reported that API attacks rose 104% in the first half of 2025 and 873% across 2024 in one global dataset. Those figures do not establish that every API is unsafe. They do show why API testing must be part of the standard assessment, with automated checks helping teams repeat authorization tests after releases without adding headcount.
What a mature program measures
A useful service model tracks whether the provider can:
- Establish ownership: Assign each issue to the team controlling the affected code, identity policy, or infrastructure.
- Prioritize exposure: Distinguish authorization failures and exploitable injection from low-impact information disclosure.
- Retest reliably: Reproduce the original attack path after a fix, using the same role, object, parameters, and response checks.
- Preserve evidence: Store requests, responses, screenshots, timestamps, and retest results for technical and audit audiences.
- Detect regression: Re-run meaningful checks after releases instead of relying on one annual assessment.
For small organizations establishing a baseline, practical tips for website security can support basic hygiene. Beyond that baseline, MSSPs need repeatable testing, accountable remediation workflows, and systematic verification at scale. Consistent evidence also makes compliance mapping more defensible when auditors ask how findings were assigned, fixed, and retested.
Mapping the Modern Threat Landscape
The OWASP Top Ten remains the most useful common language for web application security reporting. The OWASP Top Ten 2025 places Broken Access Control first and maps it to 34 CWEs, with more occurrences in applications than any other category. The project began in 2003, and its continuing value comes from turning recurring implementation failures into a shared testing and reporting framework.
Access control deserves special treatment because scanners can confirm obvious exposure but often struggle with business rules. A tester must understand which user should access which object, which role can perform which operation, and whether the same policy applies through every API version and workflow.
The categories that change testing priorities
Injection still matters. OWASP's 2025 injection guidance explains that risk appears when applications pass untrusted input to an interpreter as executable structure, especially through dynamic or non-parameterized queries, missing server-side validation, or direct concatenation into database, command-line, or ORM logic (OWASP Injection guidance). Yet an authorization flaw can expose legitimate data through a perfectly valid request, which makes it harder to detect with signature-based scanning.
SSRF also deserves attention in cloud-connected applications. The OWASP 2021 framework introduced SSRF as A10:2021, reflecting its importance as a server-side trust-boundary failure (OWASP API Security project materials). A tester should examine URL fetchers, webhook handlers, document importers, image processors, and integrations that allow the application to make outbound requests.
| Category | Primary Risk | Detection Complexity |
|---|---|---|
| Broken access control | Unauthorized records, functions, or administrative actions | High, requires role and workflow analysis |
| Injection | Data exposure or command execution through interpreter abuse | Moderate to high, depending on context |
| Stored XSS | Script execution in later users' browsers | Moderate, requires persistence and output-context testing |
| SSRF | Server-side access to unintended internal or external resources | High, requires trust-boundary and egress analysis |
| Authentication failures | Account takeover or session abuse | Moderate to high, especially across token flows |
| Security misconfiguration | Exposed services, unsafe defaults, or excessive privileges | Moderate, but scope can be broad |
| Vulnerable components | Exploitation of outdated libraries or frameworks | Lower for identification, higher for exploit validation |
The 2021 OWASP list provides standardized reporting names, including A01 Broken Access Control, A02 Cryptographic Failures, A03 Injection, A04 Insecure Design, A05 Security Misconfiguration, A06 Vulnerable and Outdated Components, A07 Identification and Authentication Failures, A08 Software and Data Integrity Failures, A09 Security Logging and Monitoring Failures, and A10 Server-Side Request Forgery (OWASP standardized list).
API testing needs its own checklist
OWASP's API Security Top Ten for 2023 puts Broken Object Level Authorization at API1 and Broken Authentication at API2 (OWASP API Security project). It also includes unrestricted resource consumption, SSRF, and unsafe consumption of APIs. That ordering reflects how API assessments should be scoped: begin with identity, object ownership, function permissions, and abuse of valid workflows before treating injection as the entire test.
Recorded Future observed 161 distinct exploited vulnerabilities in the first half of 2025, compared with 136 vulnerabilities publicly listed in CISA's KEV catalog during the same period, according to the OWASP 2025 introduction (OWASP Top Ten 2025 introduction). For an MSSP, the practical implication is clear. Verification should cover more than the vulnerabilities already present in a familiar catalog.
Exploitation Mechanics and Business Impact
A report becomes useful when the client can understand how the vulnerability behaves in a real workflow. Severity labels help prioritize, but an evidence-backed narrative explains what an attacker can submit, what the application does with it, and which business boundary fails.
Stored XSS turns persistence into reach
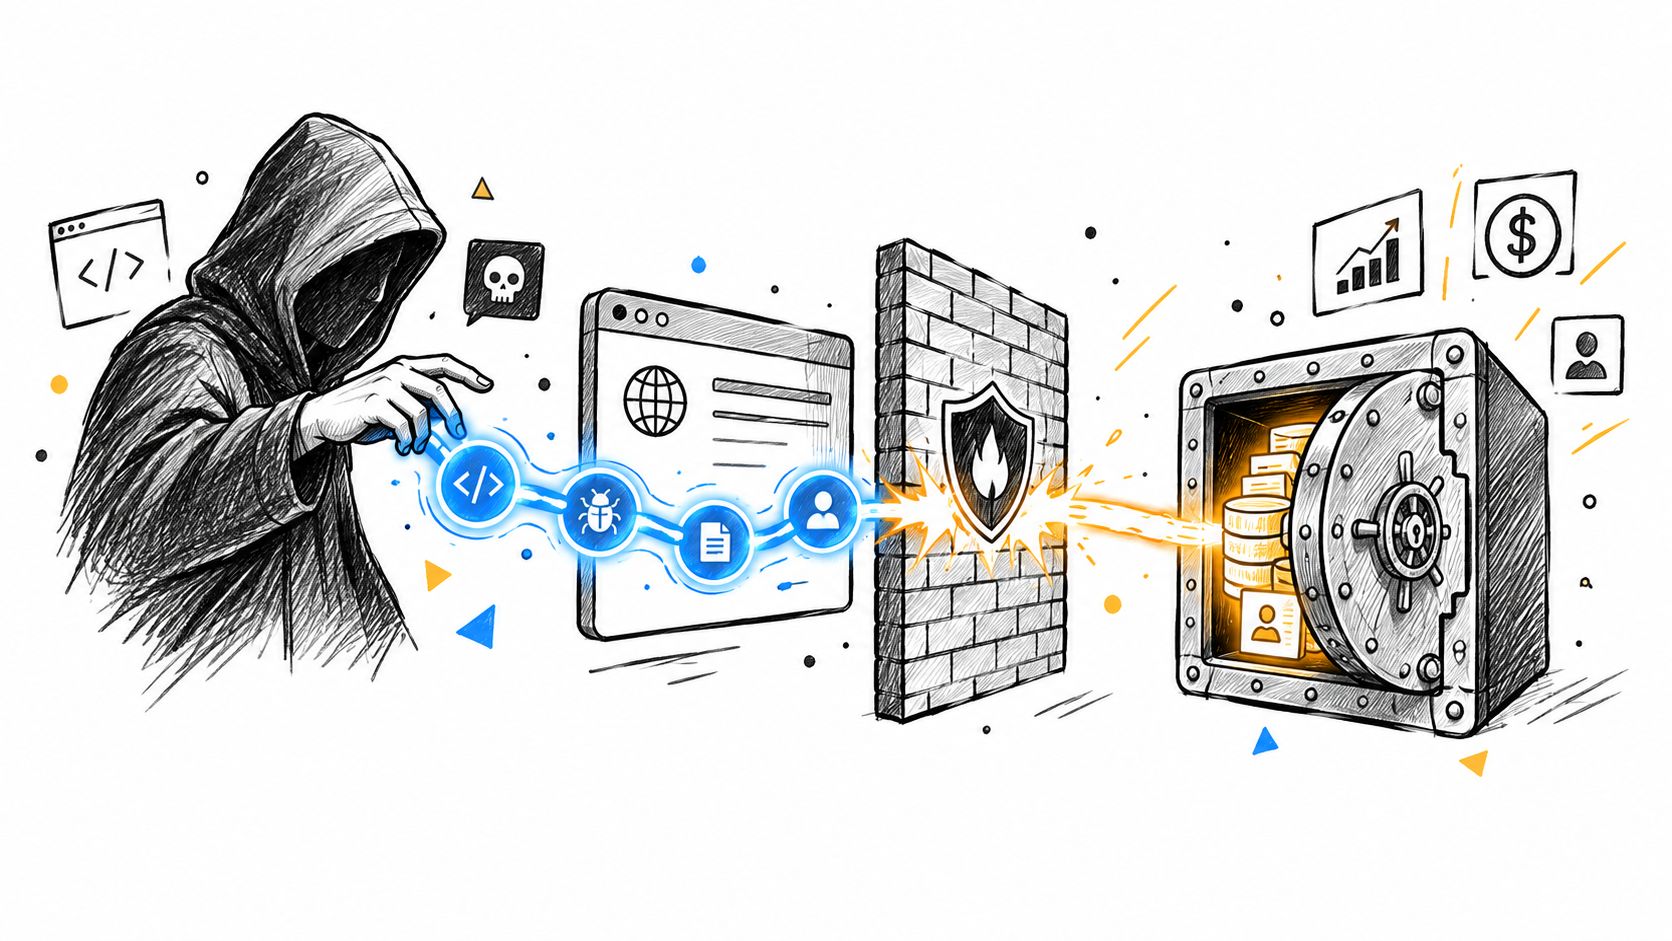
Stored XSS begins with an application accepting untrusted input, saving it, and later rendering it without correct filtering or context-aware encoding. A tester might place a payload in a support-ticket description, profile field, or shared comment. The application stores that content, and every later viewer receives a response that causes script execution in the application's origin.
OWASP identifies stored XSS as the most dangerous XSS variant because one successful stored payload can trigger across subsequent views and affect multiple users in a multi-user application (OWASP XSS testing guidance). Potential consequences include session theft, content defacement, and unauthorized actions in a victim's browser. The pentest report should show the input location, storage behavior, rendering context, affected roles, and the safe retest result.
Injection changes data into instructions
Injection occurs when the server passes hostile input to an interpreter as executable structure rather than data. In a database search, a tester may alter a parameter and observe whether the application changes query behavior, reveals records, or returns an error that exposes implementation details. In command or ORM logic, concatenated input can produce a similar boundary failure.
The technical fix is not “sanitize everything” as a vague instruction. Developers need positive server-side validation, parameterized access, and context-aware escaping, supported by tests that confirm rejected input remains data. The web application attack reference can help teams connect individual attack patterns to broader assessment planning.
BOLA exposes valid objects to the wrong user
Broken Object Level Authorization is often less theatrical than injection. A user authenticates normally, requests their own invoice, and receives a response containing an object identifier. The tester changes that identifier to another permitted-looking value and checks whether the server verifies ownership rather than merely validating that the object exists.
In REST, the weakness may appear in an endpoint that accepts an object ID. In GraphQL, it may sit inside a resolver that returns records without enforcing the caller's relationship to each object. The impact can range from one unauthorized record to broad customer-data exposure, depending on enumeration controls and the consistency of authorization checks.
The most valuable evidence often proves that the attacker used a valid account and a valid request, but crossed a boundary the business expected the server to enforce.
A strong report records the original role, the altered object reference, the response difference, and the authorization rule that should have applied. That evidence gives developers a precise regression test instead of a generic warning about “insecure API access.”
Detection and Penetration Testing Approaches
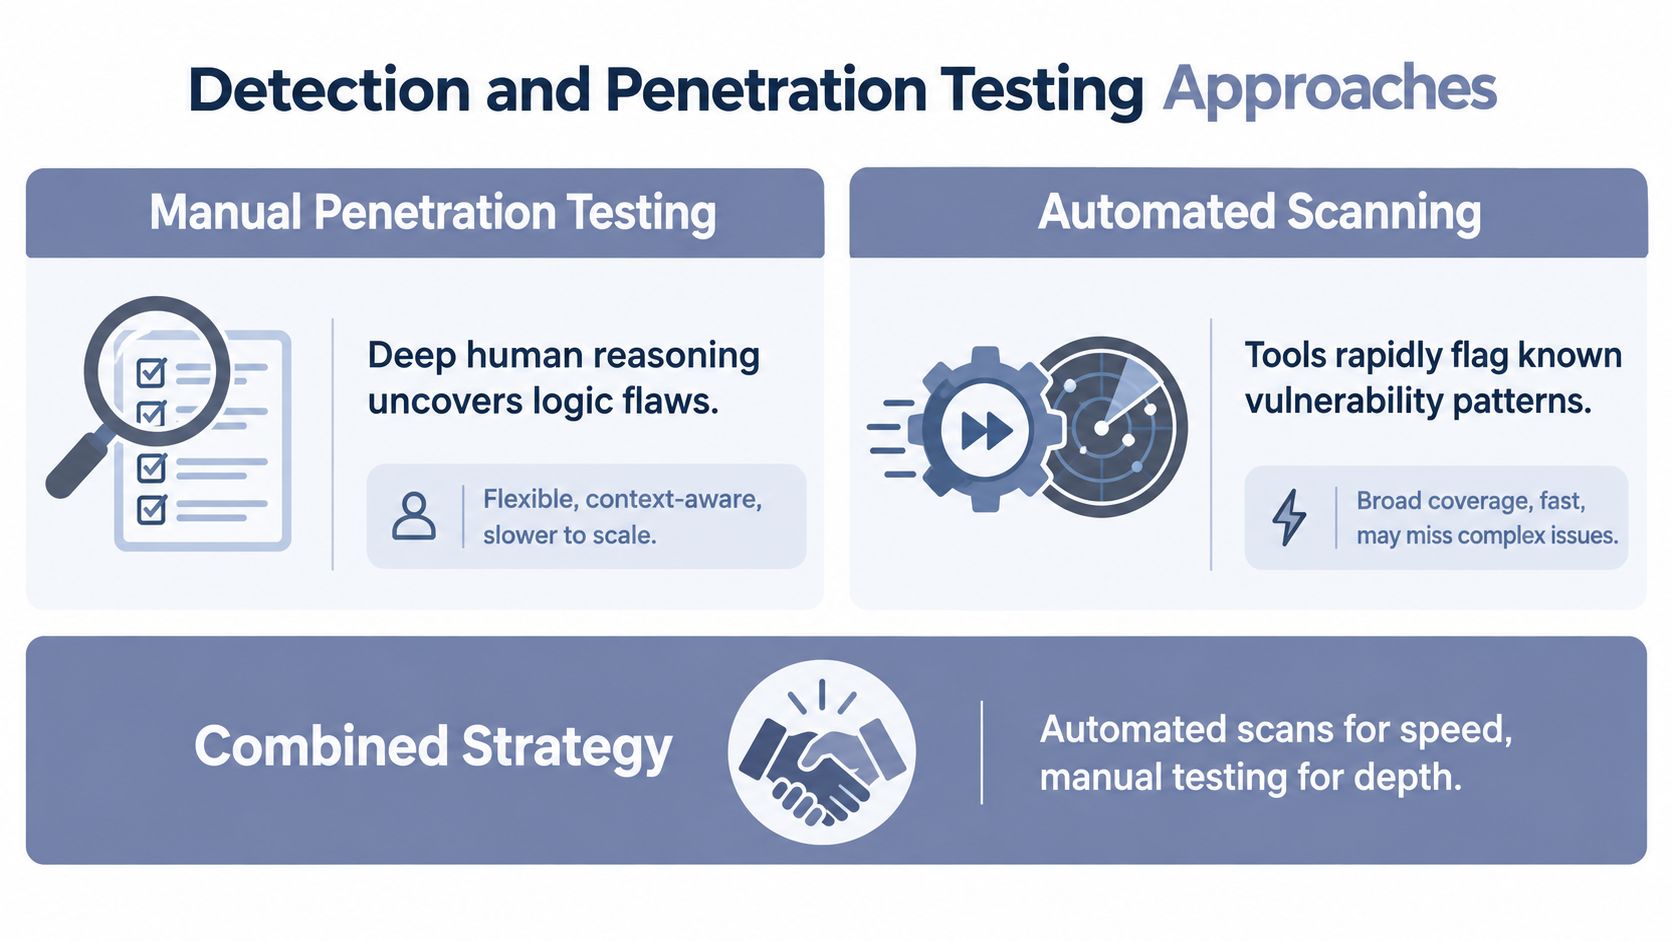
Manual penetration testing and automated scanning solve different problems. Treating them as substitutes creates predictable weaknesses. Manual testers bring judgment to undocumented workflows and business logic, while automated systems provide repeatability across large inventories and frequent releases.
Where manual testing earns its cost
A senior tester should lead the areas where context determines the result:
- Role analysis: Compare permissions across anonymous users, standard accounts, administrators, support staff, and service identities.
- Workflow abuse: Test approval, refund, invitation, export, password recovery, and account-linking processes as sequences rather than isolated requests.
- API relationship testing: Compare REST and GraphQL behavior across object types, tenants, versions, and client applications.
- Business impact validation: Demonstrate whether a finding affects confidential data, privileged actions, financial operations, or service availability.
Manual work is flexible and insightful, but it doesn't scale well when a provider must retest many customers after every deployment. It also produces inconsistent coverage when different consultants document the same checks in different ways.
Where automation earns its place
Automated testing can enumerate routes, replay known patterns, inspect responses, coordinate tools, and preserve evidence without requiring a senior consultant to repeat every mechanical step. DAST can probe running applications, while SAST, IAST, and software composition analysis add code and dependency context. None of these should be treated as proof that complex authorization is correct.
A practical MSSP model uses automation for discovery, baseline checks, regression testing, evidence capture, and first-pass prioritization. Human testers then investigate high-risk workflows, resolve ambiguity, and review whether the observed behavior matches the client's business rules. ThreatExploit AI is one option in this category. It supports web applications, REST and GraphQL APIs, reconnaissance, exploitation, verification, and evidence-backed reporting through an agentic testing workflow.
A delivery pattern that controls cost
The strongest operating model separates repeatable checks from judgment-heavy assessment:
- Baseline the application: Maintain authenticated and unauthenticated inventories, API specifications, roles, and known trust boundaries.
- Run automated coverage: Test routes, parameters, common OWASP patterns, authentication flows, and previously confirmed findings.
- Escalate uncertain results: Send authorization anomalies, chained behaviors, and high-impact responses to a human tester.
- Retest after remediation: Replay the original evidence and test nearby variants to catch incomplete fixes.
- Report by audience: Give executives risk and ownership, developers reproduction steps, and auditors control-linked evidence.
For background on scoping this model, web application penetration testing resources provide a practical reference point.
Remediation Workflows and Secure Development
A remediation ticket is useful only when an engineer can turn it into a code or policy change and a tester can prove the result. The target is the violated control boundary, not merely the input that exposed it. Delayed fixes leave API routes, roles, and business workflows exposed while teams assume the original finding is already contained.
Start with ownership and a reproducible test
Assign the issue to the team that owns the affected code or policy. Record the endpoint, role, object, request, response, expected authorization rule, and a minimal safe reproduction. For an MSSP, that package connects discovery to engineering and gives retesting a stable baseline.
Developers should add a regression test with the fix or before it. An authorization test can verify that a user retrieves their own object but receives a denial for another tenant's object. A workflow test should cover the permitted path, the forbidden transition, and any alternate API route that reaches the same operation.
Apply controls at the server boundary
A hidden client-side control provides no authorization. The server must enforce permissions for every sensitive object and function, including requests assembled outside the user interface. For injection and XSS, the implementation should follow the controls already established during development. The next step is to place those controls in shared libraries, typed interfaces, and secure defaults, so individual endpoints do not reintroduce ad hoc filters.
Put API authorization into the delivery pipeline
An OpenAPI document check cannot verify whether a caller may access a particular object or invoke a sensitive function. Build pipelines should exercise role matrices, object ownership, function permissions, token scope, rate limits, and error handling. GraphQL pipelines should test resolver authorization and confirm that nested objects cannot bypass the policy applied to the parent request.
A practical sequence is:
- Pull request stage: Run static checks, dependency analysis, secret detection, and unit tests for authorization rules.
- Build stage: Deploy an isolated target and run authenticated API tests with representative roles.
- Pre-release stage: Execute business-logic and abuse-case tests for high-risk workflows.
- Post-release stage: Repeat baseline tests, compare the evidence with the previous build, and open a new issue when behavior still violates the rule.
Teams formalizing this process can use best practices for API security as a planning reference. Automated replay makes verification repeatable across clients and releases, while human testers remain focused on ambiguous authorization chains and business impact. The operating result is a closed loop: an owner, a fix, a regression test, and evidence that the exposed path now enforces the intended policy.
Compliance Mapping and Audit Readiness
Penetration testing produces more value when its evidence can serve both engineers and auditors. A technical finding should map to the control objective it affects, while preserving enough detail for a qualified reviewer to reproduce the conclusion.
The OWASP naming structure gives MSSPs a useful application-risk taxonomy. A broken authorization finding can be reported under Broken Access Control, then connected to the client's access governance, least-privilege, change-management, and monitoring obligations. An injection finding can support evidence around secure development, input validation, testing, and vulnerability management.
Build the evidence package once
A repeatable report should include:
- Executive context: A concise explanation of affected systems, business impact, ownership, and remediation status.
- Technical proof: Reproduction steps, request and response details, screenshots, affected roles, and safe payload handling.
- Control references: The relevant OWASP category and applicable PCI-DSS, SOC 2, HIPAA, or ISO 27001 control references.
- Retest history: Original finding, remediation date, retest method, result, and any residual exposure.
- Scope record: Target, environment, credentials or roles used, exclusions, testing window, and limitations.
Manual mapping creates avoidable rework, especially when a provider serves clients with different frameworks. Automated report generation can attach control references and preserve technical evidence while the consultant reviews whether the mapping fits the client's actual scope.
Treat reports as operational records
Auditors need more than a severity label. They need to see what was tested, what failed, how the organization responded, and whether the correction was verified. A structured PDF or JSON output can support client delivery, ticketing, dashboards, and recurring assessments without rewriting the same finding for each audience.
That changes the commercial role of a pentest. The assessment becomes evidence for remediation governance and vendor due diligence, not merely an annual document stored until the next audit request.
Scaling Security Operations for MSSPs
MSSPs can't scale web application security by assigning every recurring check to a senior pentester. Manual expertise remains essential, but using it for route enumeration, screenshot collection, repetitive retests, and report formatting consumes capacity that should go toward judgment-heavy work.
The viable model is continuous, agentic testing with human oversight. An automated engine can coordinate reconnaissance, exploit attempts, verification, and evidence collection across repeatable environments. Consultants can then investigate authorization drift, review business impact, and communicate remediation decisions to the client.
Design the service around repeatability
A scalable offering needs a consistent operating spine:
- Standardized intake: Capture application URLs, API documentation, test accounts, role definitions, environments, exclusions, and client approval.
- Reusable test profiles: Maintain checks for OWASP categories, authentication, authorization, injection, XSS, SSRF, exposed services, and known client-specific risks.
- Evidence-backed verification: Store the request, response, screenshot, affected role, and retest outcome rather than only a scanner alert.
- Human escalation: Route ambiguous authorization behavior, chained findings, and sensitive production concerns to an experienced tester.
- Client-facing reporting: Produce executive and technical views from the same validated finding record.
This structure reduces inconsistency without pretending that automation understands every business rule. It also lets a provider run recurring assessments after application changes, rather than waiting for a point-in-time engagement.
Use automation to expand expertise, not hide its absence
The commercial benefit comes from shifting senior effort to the places where it has the greatest effect. A consultant who no longer spends the day repeating baseline scans can review more authorization matrices, challenge weak remediation explanations, and help developers create durable regression tests.
ThreatExploit AI is designed for security service providers and supports web applications, including REST and GraphQL APIs, with automated reconnaissance, exploitation, verification, and reporting. Its platform materials describe dedicated testing infrastructure, orchestration across more than 60 tools, PDF and JSON reporting, and compliance mapping for frameworks including HIPAA, SOC 2, PCI-DSS, and ISO 27001. Those capabilities fit a provider model that needs repeatable evidence and multi-tenant delivery, but every MSSP should validate coverage, authorization safety, and reporting quality against its own service standards.
Operating principle: Automate the repeatable path, reserve human judgment for the uncertain path, and make every remediation claim pass through verification.
The result is a security service that can support more clients without lowering assessment quality. Providers can offer recurring testing, remediation retests, and audit-ready reporting as one connected workflow instead of selling isolated scans and manually assembled documents.
ThreatExploit AI automates reconnaissance, exploitation, verification, and evidence-backed reporting for web applications and REST or GraphQL APIs, helping MSSPs turn repeatable testing into a continuous service. Visit ThreatExploit AI to evaluate how its agentic platform can expand testing capacity, support compliance mapping, and reduce manual remediation verification work.